Wednesday, September 23, 2026 · Cyber news, in panels.
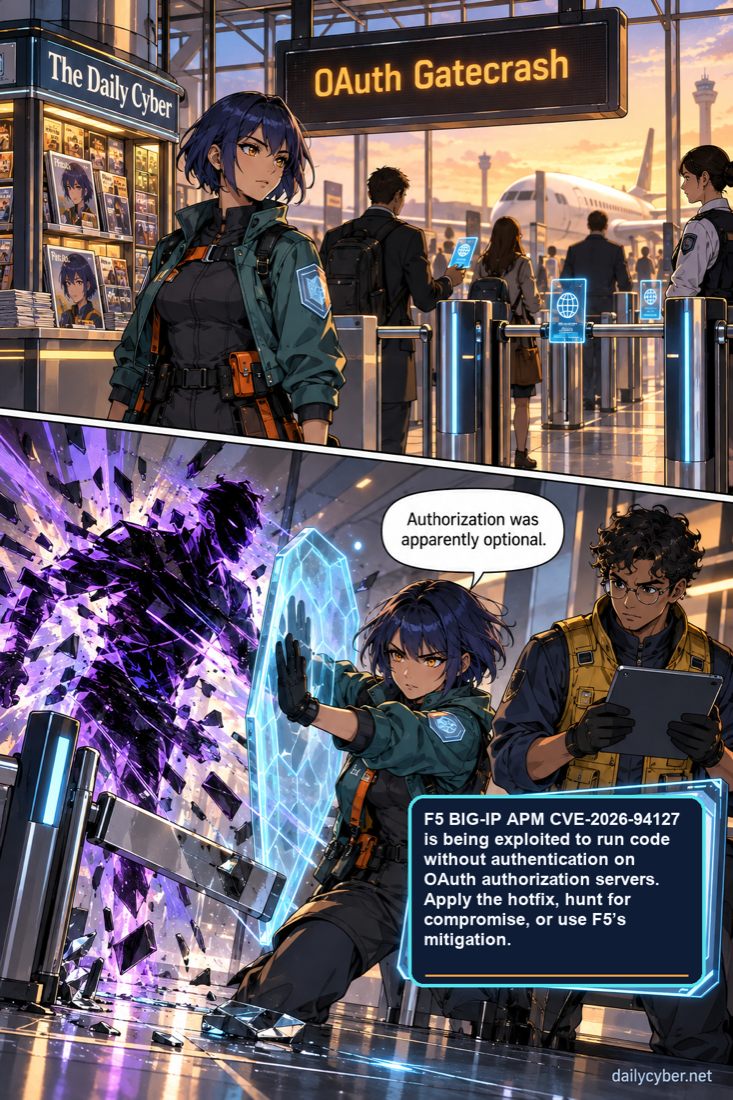
F5 patched actively exploited CVE-2026-94127 in BIG-IP APM OAuth authorization-server deployments, where unauthenticated attackers could gain remote code execution; apply the hotfix or vendor mitigation and review systems for compromise.

F5 BIG-IP OAuth Gatecrash

F5 patched actively exploited CVE-2026-94127 in BIG-IP APM OAuth authorization-server deployments, where unauthenticated attackers could gain remote code execution; apply the hotfix or vendor mitigation and review systems for compromise.

Get tomorrow's comic in your inbox

One panel a day. No spam, unsubscribe with one click.